Enabling Secure Boot is a critical step for users looking to upgrade to Windows 11 or ensure their system remains protected against low-level malicious software. As a security standard developed by the PC industry, this feature helps ensure that a device boots using only software that is trusted by the Original Equipment Manufacturer (OEM).
For those using an ASUS motherboard, the process is typically handled within the UEFI BIOS utility. While the interface might look slightly different depending on whether you are using a ROG (Republic of Gamers), TUF Gaming, or Prime series board, the fundamental logic remains consistent across the ASUS ecosystem.
Understanding the Role of Secure Boot in System Security
Secure Boot acts as a gatekeeper during the initial power-on process of your computer. When you press the power button, the motherboard firmware performs a series of checks to verify the digital signatures of the bootloader, kernel, and critical drivers.
If the signatures do not match the authorized keys stored in the firmware, the system will refuse to load the operating system. This prevents rootkits and bootkits from compromising your machine before the operating system even has a chance to load its own security defenses.
On an ASUS system, this feature works in tandem with the UEFI (Unified Extensible Firmware Interface) environment. Unlike the legacy BIOS, which was limited in its security capabilities, UEFI provides a more robust framework for modern hardware.
By ensuring that your boot state is correctly configured, you create a chain of trust that starts from the hardware level. This is particularly important for users who handle sensitive data or play online games that require anti-cheat software, which often mandates a secure environment to function correctly.
Accessing the ASUS UEFI BIOS Utility
Before you can modify any settings, you must first enter the BIOS interface. The process is straightforward but requires precise timing during the boot sequence.
When you restart your computer, keep an eye on the monitor. As soon as the ASUS logo appears, you need to initiate the command to enter the firmware setup.
To enter the BIOS, repeatedly tap either the Delete key or the F2 key on your keyboard immediately after turning on your power supply. If you miss the window, your system will proceed to load Windows; simply restart the computer and try again.
Once you have successfully entered the BIOS, you will likely see the “EZ Mode” screen, which provides a high-level overview of your hardware, including CPU temperature, fan speeds, and memory status. To access the advanced configuration required to enable secure features, you will need to switch to the “Advanced Mode” by clicking the corresponding button or pressing the F7 key on your keyboard.
Navigating to the Secure Boot Configuration
Once you are in Advanced Mode, the interface will present you with several tabs, such as Main, Ai Tweaker, Advanced, Monitor, Boot, and Tool. The specific location of the security settings can vary slightly depending on your motherboard model, but it is almost always found under the “Boot” tab.
Navigate to the “Boot” menu using your arrow keys or mouse. Within this menu, look for a sub-menu labeled “Secure Boot.” If you do not see it immediately, look for a category named “CSM” (Compatibility Support Module).
It is a vital note that for Secure Boot to be configurable, CSM must typically be disabled. CSM is designed to provide compatibility for older operating systems and hardware that do not support UEFI.
Because Secure Boot relies exclusively on the UEFI environment, the two features are mutually exclusive. If CSM is enabled, the option to configure Secure Boot may be hidden or greyed out.
Configuring Key Management and Platform Mode
Inside the Secure Boot sub-menu, you will find settings related to the “OS Type” and “Key Management.” The “OS Type” setting usually offers two choices: “Windows UEFI mode” and “Other OS.”
To ensure proper functionality, you must select “Windows UEFI mode.” This tells the motherboard firmware to expect a modern operating system that supports UEFI security protocols.
The “Key Management” section is where you interact with the platform keys. These keys are cryptographic signatures that verify the integrity of your software. For most home users, the default settings are sufficient, and you should not need to manually install or delete keys unless you are performing specialized development work.
If you find that the option to enable the feature is still restricted, you may need to reset the “Platform Key” (PK) to its factory default state. This action reinstalls the standard keys provided by ASUS, effectively clearing any custom configurations that might be preventing the system from verifying the boot state correctly.
Troubleshooting Common ASUS Secure Boot Issues
Many users encounter a scenario where the Secure Boot state remains “Disabled” even after they have followed the standard steps. This is often due to the interaction between the motherboard’s firmware and the partition style of your primary storage drive.
Secure Boot requires that your boot drive be formatted as a GPT (GUID Partition Table) disk. If your drive is still using the older MBR (Master Boot Record) format, the system will not be able to utilize UEFI features effectively, and Secure Boot will fail to initialize.
If you are facing a situation where the menu is greyed out, verify the following:
- Ensure that CSM is fully disabled in the Boot menu.
- Check that your primary drive is converted to a GPT partition style.
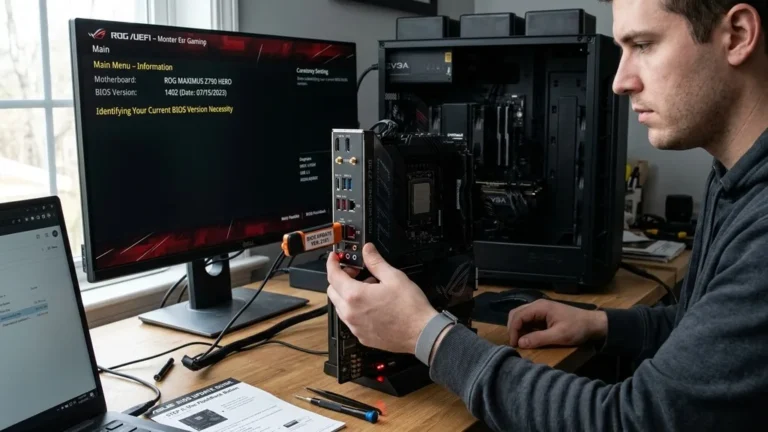
- Confirm that you are running the latest version of the BIOS firmware for your specific motherboard model.
- Verify that the “Secure Boot Mode” is set to “Standard” rather than “Custom” unless you have specific requirements for custom keys.
Updating your BIOS is often a highly effective way to resolve persistent configuration issues. ASUS provides detailed support pages and utility tools to help users flash their firmware safely. You can find more information on managing your system’s hardware configuration at the official ASUS Support portal, which serves as a reliable resource for all hardware-related inquiries.
Saving Your Changes and Exiting the BIOS
After you have adjusted the settings to your satisfaction, you must commit these changes to the non-volatile memory of the motherboard. Simply exiting the BIOS without saving will revert your system to its previous state, effectively undoing all the work you just performed.
Navigate to the “Exit” tab or press the F10 key on your keyboard. A dialog box will appear, asking if you wish to save the changes and reset the system. Select “Save & Reset” or “Save Changes and Exit.”
Your computer will then reboot. As it starts up, the UEFI environment will verify the system’s integrity against the security keys you have configured. If everything is set up correctly, Windows will boot normally, and you can verify that the feature is active by checking the “System Information” app within Windows.
Simply type “msinfo32” into your start menu search bar and look for the “Secure Boot State” entry. It should read “On” or “Enabled.”
The Interaction Between TPM 2.0 and Secure Boot
In the modern landscape of Windows 11, Secure Boot is rarely discussed without its partner: the Trusted Platform Module (TPM). While Secure Boot ensures the integrity of the software being loaded, TPM 2.0 provides a hardware-based vault for cryptographic keys and system health measurements. On most modern ASUS motherboards, the TPM is integrated into the processor (fTPM for AMD or PTT for Intel).
To have a fully compliant system for modern operating systems, you must enable both of these features. While Secure Boot is managed in the “Boot” menu, the TPM setting is usually found in the “Advanced” or “AMD fTPM configuration” / “Intel Platform Trust Technology” sections of the BIOS. Both act as pillars of modern system security.
Enabling one without the other may leave your system vulnerable or incompatible with software that requires a fully hardened environment. When configuring these, always ensure that your firmware is up-to-date, as security patches for the TPM module are frequently included in BIOS updates released by the manufacturer.
Comparison of UEFI and Legacy BIOS Modes
Understanding why these modern security features require a transition from legacy systems is essential for troubleshooting. The following table highlights the key differences that impact how you manage your motherboard settings.
| Feature | Legacy BIOS | UEFI BIOS |
|---|---|---|
| Boot Process | BIOS loads MBR | UEFI loads GPT/EFI partitions |
| Security | None (No signature checks) | Secure Boot (Signature verification) |
| Interface | Keyboard-only, basic text | Graphical, mouse-supported |
| Drive Support | Max 2.2TB per partition | Supports massive drives (up to 9ZB) |
As shown in the table, the shift to UEFI is not just about security; it is about modernizing the entire boot flow. By moving away from the limitations of legacy BIOS, ASUS motherboards can provide a faster, more secure, and more versatile experience. This is why the system requires you to disable CSM, as keeping that module active forces the motherboard to emulate the older, less secure environment, which inherently conflicts with the requirements of Secure Boot.
Frequently Asked Questions
Why is my Secure Boot option greyed out in the ASUS BIOS?
This usually happens because the Compatibility Support Module (CSM) is currently enabled. Secure Boot requires a pure UEFI environment. To fix this, navigate to the Boot menu, find the CSM settings, set it to “Disabled,” save your changes, and restart the BIOS to unlock the Secure Boot menu.
Do I need to enable Secure Boot for Windows 11?
Yes, Secure Boot is a mandatory hardware requirement for Windows 11. Along with a TPM 2.0 module, it ensures that your system meets the security standards defined by Microsoft to protect against modern cyber threats and to support features like Virtualization-Based Security (VBS) and Device Guard.
Will enabling Secure Boot delete my data?
No, changing the Secure Boot setting in your BIOS will not delete any files or data on your hard drive. However, if your drive is currently formatted as MBR and you need to convert it to GPT to satisfy UEFI requirements, you must back up your data before performing that conversion.
What should I do if my PC won’t boot after changing these settings?
If your system fails to boot, you may have changed a setting that is incompatible with your current drive configuration. Simply re-enter the BIOS by pressing F2 or Delete during startup, revert the settings to their previous state (specifically re-enabling CSM if necessary), save, and your system should boot as before.
The process of securing your computer is a vital practice in today’s digital environment. By following the steps to configure your ASUS motherboard properly, you are taking a proactive stance in protecting your system from unauthorized boot-time modifications. While the BIOS environment can seem intimidating at first, understanding the relationship between UEFI, CSM, and Secure Boot allows you to manage your hardware with confidence.
Always remember to proceed with caution when modifying firmware settings and ensure that your primary storage is correctly partitioned to support these modern security standards. With these steps completed, your system will be better equipped to handle the demands of modern operating systems and security protocols.