Ensuring your computer meets modern security standards is essential, especially with the transition to newer operating systems. If you are trying to upgrade to Windows 11 or simply want to harden your system against rootkits and unauthorized boot-time software, learning how to enable secure boot on MSI motherboard hardware is a critical skill.
Secure Boot is a security standard developed by members of the PC industry to help ensure that a device boots using only software that is trusted by the Original Equipment Manufacturer (OEM). On an MSI motherboard, this functionality is managed within the Click BIOS 5 interface, which provides a graphical environment to adjust your system’s low-level settings.
Understanding the Role of UEFI and Secure Boot
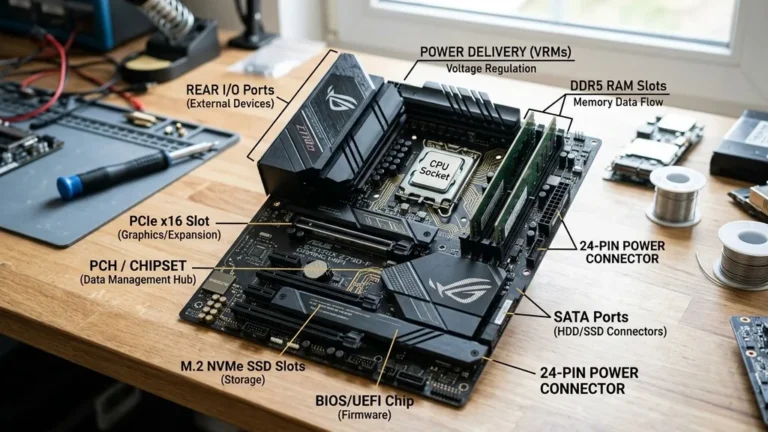
At the heart of the modern PC boot process is the UEFI (Unified Extensible Firmware Interface). Unlike the aging legacy boot systems of the past, UEFI provides a more robust, flexible, and secure environment for your hardware to initialize before the operating system takes control. Secure Boot acts as a gatekeeper within this firmware interface.
It checks the digital signature of every piece of boot software, including UEFI firmware drivers, EFI applications, and the operating system itself. If the signature matches a trusted authority, the system proceeds; if not, the boot process is halted to prevent malicious code from executing.
To leverage this feature, your drive must be initialized using the GPT (GUID Partition Table) partition style rather than the older MBR (Master Boot Record). If your drive is still formatted as MBR, Secure Boot will likely fail to activate because the hardware cannot verify the bootloader in the way required by modern security standards. Understanding that your disk management configuration is tied directly to your firmware settings is the first step in troubleshooting any issues you might encounter during the setup process.
Navigating the MSI Click BIOS 5 Interface
Most modern MSI boards utilize the Click BIOS 5 environment. To access this, you must restart your computer and repeatedly press the “Delete” key during the initial POST (Power-On Self-Test) screen. Once inside, you will see the EZ Mode interface.
While EZ Mode provides a quick overview of your boot priority and system temperature, you will need to enter “Advanced Mode” to modify sensitive security settings. You can do this by pressing the F7 key on your keyboard.
Once you are in Advanced Mode, look for the “Settings” tab on the left-hand side. Within this menu, select “Advanced,” and then locate “Windows OS Configuration.” This is where the magic happens.
You will find options for both the BIOS mode and the Secure Boot state. It is important to remember that MSI boards often default to a “CSM” or Compatibility Support Module mode to ensure older hardware still works.
You must ensure CSM is disabled to fully utilize UEFI-based security features. If CSM is enabled, the option to toggle Secure Boot will often remain greyed out or completely invisible.
Addressing the CSM and Partition Style Requirements
A common hurdle users face when attempting to enable Secure Boot is the conflict with the Compatibility Support Module. The CSM is designed to emulate legacy BIOS environments, which is inherently incompatible with the strict signature-checking requirements of Secure Boot.
If you try to enable Secure Boot while CSM is active, the system will effectively block you. You must switch the BIOS mode from “CSM” to “UEFI” within the Windows OS Configuration menu.
However, simply switching to UEFI mode might result in your system failing to boot if your primary storage drive is formatted as MBR. This is where you must verify your partition style. You can check this in Windows by right-clicking the Start button, selecting “Disk Management,” right-clicking your disk, and viewing its “Properties” under the “Volumes” tab.
If it says “Master Boot Record,” you will need to convert the drive to GPT. Microsoft provides an official utility called MBR2GPT that allows you to perform this conversion without data loss, though it is always wise to back up your critical files before touching disk partitions.
Managing System Modes: Setup vs. User
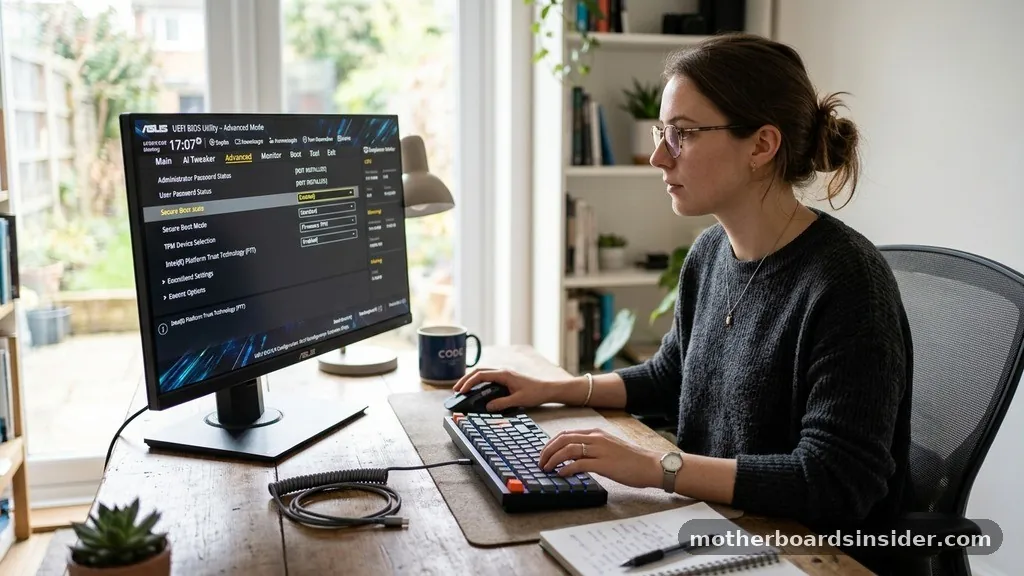
The state of your firmware’s security keys is defined by the System Mode. When you are configuring Secure Boot, you will often see references to Setup Mode and User Mode.
Setup Mode is a state where you are allowed to add or modify the cryptographic keys—specifically the Platform Key (PK), the KEK (Key Exchange Key), and the signature databases (db and dbx). These keys are the heart of the verification process; they act as the “trusted list” that the motherboard consults during startup.
If your system is in “User Mode,” it means the security keys are already installed, and the firmware is in a locked, protected state. If you find your system stuck in “Setup Mode” and cannot enable Secure Boot, you may need to look for an option in the BIOS labeled “Enroll all Factory Default Keys.” Selecting this option will install the standard Microsoft and MSI manufacturer keys, effectively transitioning your system into User Mode and allowing you to toggle the Secure Boot switch to “Enabled.”
The Crucial Link Between Secure Boot and TPM 2.0
For users aiming to meet Windows security requirements, Secure Boot is only half of the equation. You also need to ensure that the Trusted Platform Module (TPM 2.0) is enabled.
While Secure Boot verifies the integrity of the software, the TPM provides a hardware-based vault for storing sensitive data, such as encryption keys for BitLocker or authentication credentials. On MSI motherboards, this is usually found under the “Security” or “Trusted Computing” tab within the Advanced BIOS settings.
It is important to note that many modern processors have a “firmware TPM” (fTPM) built into the CPU, which is what you will likely be enabling. Ensure that you are selecting the option to enable the TPM device, often labeled as “AMD fTPM” on Ryzen systems or “Intel PTT” on Intel-based boards. Once both Secure Boot and TPM 2.0 are active, your system will be fully compliant with the hardware compatibility standards required for a seamless Windows 11 experience.
| Feature | Role in System Security | BIOS Location |
|---|---|---|
| Secure Boot | Verifies OS bootloader integrity | Windows OS Configuration |
| TPM 2.0 | Hardware-based cryptographic storage | Security / Trusted Computing |
| CSM | Legacy compatibility (must be OFF) | Windows OS Configuration |
Troubleshooting Missing Options in BIOS
If you have followed the steps above and still cannot find the Secure Boot toggle, do not panic. The most frequent cause is that the BIOS is still in “Legacy” mode.
Even if you think you have switched it to UEFI, certain motherboard settings can override your choices if a legacy device is detected. For instance, some older graphics cards do not support UEFI GOP (Graphics Output Protocol), which forces the motherboard to drop back into CSM mode automatically.
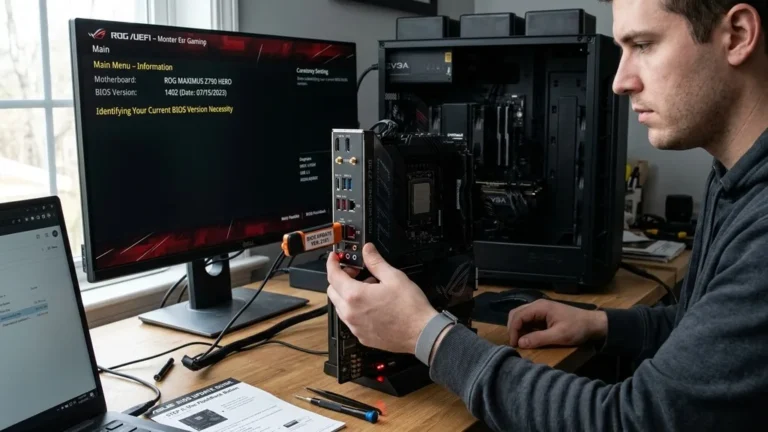
If you are experiencing this, you may need to perform a firmware update. MSI regularly releases BIOS updates that improve hardware compatibility and fix bugs related to Secure Boot implementation.
You can download the latest BIOS file from the official MSI support website, place it on a FAT32-formatted USB drive, and use the M-Flash tool within the BIOS to update your system. A newer version of the firmware often resolves issues where the Secure Boot menu options are hidden or unresponsive.
Securing Your BIOS with an Administrator Password
Once you have successfully enabled Secure Boot and configured your TPM, it is highly recommended that you set a BIOS administrator password. Without a password, anyone with physical access to your machine can simply enter the BIOS, disable Secure Boot, and potentially bypass your system’s security measures. By setting a password, you ensure that only authorized individuals can modify the low-level firmware settings.
Keep in mind that if you forget this password, there is often no easy way to recover it. On many motherboards, you would have to clear the CMOS by removing the coin-shaped battery from the board for several minutes, which would reset all your BIOS settings to their factory defaults—including the Secure Boot settings you just worked so hard to configure. Always write your password down and store it in a secure location, such as a password manager.
Summary of Steps for Success
To summarize, the process of enabling Secure Boot on your MSI board is a logical sequence of settings adjustments. First, ensure your drive uses the GPT partition style. Second, enter the BIOS, switch to Advanced Mode, and disable the CSM.
Third, ensure your firmware is in UEFI mode and that you have enrolled the factory default security keys. Finally, verify that your TPM is active. By following these steps, you create a chain of trust that starts from the moment you press the power button and extends all the way into the operating system.
- Verify your drive is partitioned as GPT using Disk Management.
- Enter BIOS (press Del during startup) and switch to Advanced Mode (F7).
- Navigate to Settings > Advanced > Windows OS Configuration.
- Disable CSM and set BIOS mode to UEFI.
- Ensure “Secure Boot” is set to Enabled and keys are enrolled.
- Enable fTPM or PTT under the Security or Trusted Computing menu.
- Save changes and exit (F10) to apply the new configuration.
Frequently Asked Questions
Why is the Secure Boot option greyed out in my BIOS?
This usually happens because the Compatibility Support Module (CSM) is currently enabled, or your system is in “Setup Mode” without factory keys enrolled. Disable CSM in the Windows OS Configuration menu and ensure you select the option to enroll the default factory keys to unlock the setting.
Do I need to reinstall Windows after enabling Secure Boot?
If your disk is already formatted as GPT, you do not need to reinstall Windows. However, if your disk is currently MBR, you must convert it to GPT first. If you try to boot with UEFI/Secure Boot enabled on an MBR disk, the system will not find a valid boot device.
What should I do if my PC fails to boot after these changes?
If your PC fails to boot, it is likely due to the partition style mismatch (MBR vs GPT) or a legacy-only graphics card. You can enter the BIOS by pressing Del during the boot process, re-enable CSM, and save changes to restore access, then troubleshoot the partition style or hardware compatibility further.
Is Secure Boot enough to protect my computer?
Secure Boot is a vital layer of defense against boot-level threats, but it is not a replacement for antivirus software or good security practices. It protects the integrity of the boot process, while other security measures like TPM-backed encryption and regular software updates protect your data and running environment.
In conclusion, taking control of your motherboard’s security settings is a proactive step toward maintaining a healthy and resilient computing environment. By correctly configuring your MSI BIOS, you satisfy the requirements for modern operating systems while simultaneously closing potential security loopholes. Always remember that firmware changes should be approached with patience; if something does not work on the first try, verify each step against your specific hardware configuration, and ensure your system components are fully compatible with UEFI standards.